Real-device install and lifecycle
Install, app launch, file picker, language, update and uninstall still need evidence from multiple physical phones.
Android 0.2.0-dev is a new buildable preview. The previous Android 0.1.0 product claims did not have corresponding runnable source in this repository. This preview provides local SHA-256 file inspection and EICAR test signature only; not a production antivirus.
Official: aq.kingai.work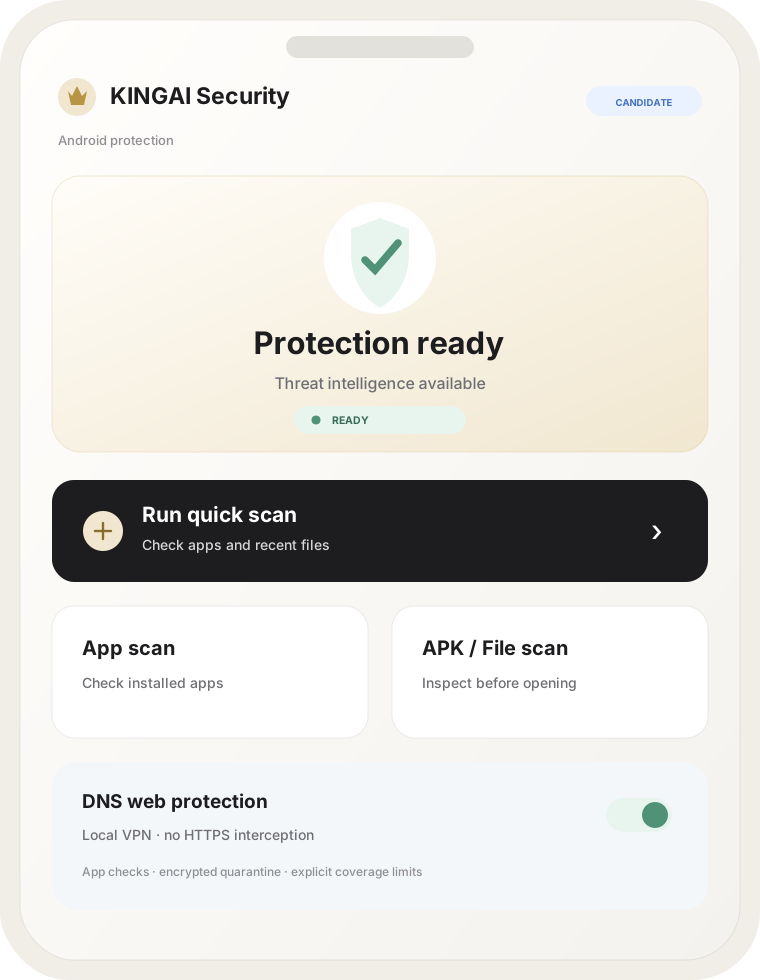
The preview APK is signed with an Android development key. It is not a Play Store package and cannot update a differently signed app with the same package name. Downloads currently reside in a private GitHub repository.
Core capabilities are checked by automated tests and emulator installation. Real-device compatibility and full antivirus coverage remain unverified.
Install, app launch, file picker, language, update and uninstall still need evidence from multiple physical phones.
Production threat signatures, signed updates, quarantine and DNS-only VPN are not implemented in Android 0.2.0-dev.
The private debug APK is not Play-signed and is not cleared for store distribution.
The actual release job must validate the live Threat DB manifest, exact schema/types, P-256 signature and time window before signing builds.
Review current status before installing a build.
aq.kingai.work